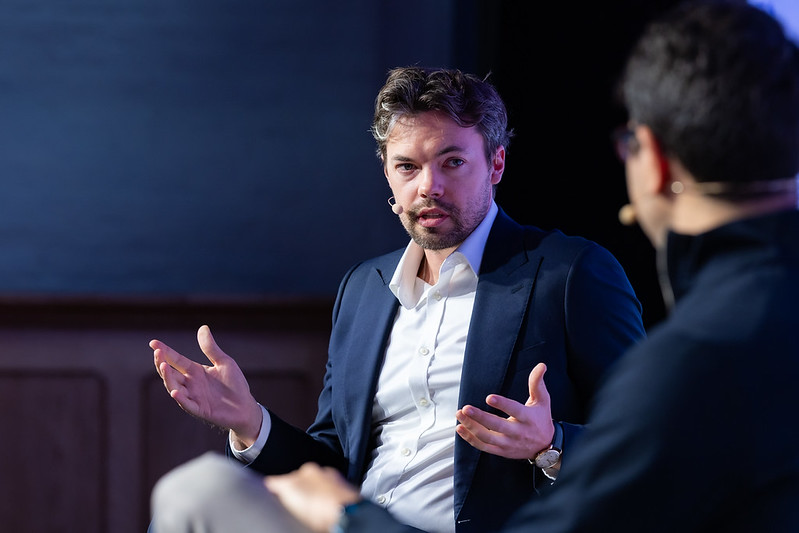
Grey-zone manoeuvres are closer than you think to disrupting everyday life, even in countries far from the frontlines of current wars, and generally while countries like the UK are swimming in data, including a lot of surveillance data, there is virtually no coordination in how that data is analysed today to respond, much less pre-empt, grey-zone attacks. That was the message from Augur CEO Harry Mead, who was on stage at Resilience Conference this week.
Technology seemingly is the answer for how to better process the clues, but it is also the problem. Mead said the network of people to carry out attacks is being pulled together over social networks — not just platforms known for organising nefarious activity like Telegram, but also ordinary, well-known consumer apps like Snapchat.
Augur is a data intelligence startup, and its research into the situation, he said, has indicated a “massive increase” in the utilisation of apps like Snapchat and Telegram to recruit young people to do the dirty work.
“We aren’t seeing the traditional proxies [used] to carry out these attacks,” he said. “We are actually seeing a massive increase in the utilisation of systems such as Telegram and Snapchat to recruit 20 year old kids to conduct everything from arson attacks on critical energy infrastructure to potential assassinations on domestic soil.”
Messaging and social media apps have become a cornerstone of how young people connect with the world these days, and that’s given them a dubious double role. They are also being used to target individuals to radicalise them, and used to connect with those looking for any means to earn some money, willing to carry out grey-zone activity. (The latter was the subject of a recent investigation into the network of “disposable agents” that were being organised and activated to carry out arson and other activities in Europe. )
“We are [now] seeing the consequence of the targeting of those individuals by Russia, by Iran,” he said.
The rise in incidents across Europe has been “staggering” in the wake of the war in Ukraine, he said, and that has finally started to focus people’s minds on the threat.
Until a few years ago, much of Europe assumed the traditional rules of warfare would apply in Ukraine: they thought that Russia, which launched its full-scale invasion of Ukraine in 2022, would focus solely on attacks there.
That has now shifted with a sharp rise in grey-zone attacks, which can come in the form of cyberattacks, arson, vandalism, drone and other incursions, disinformation, and more.
“And it doesn’t just mean defence institutions and infrastructure,” he continued. “We are starting to see a massive increase in the proliferation of attacks on civilian infrastructure.”
Between April 2022 and April 2026, Mead noted, there were 300 attacks attributed to Russia across the West. This number, in the last six months alone, was growing at a rate of 40%, “and we are not equipped to handle that.”
Grey-zone attacks, Mead pointed out, will partly continue to grow because they are a cheap way to hit at a country compared to traditional methods. They also serve as a great distraction while shaking people up and creating a chilling effect on responding.
“Paying a kid 20 grand to carry out a target assassination is significantly less expensive than an anti-aircraft system,” he said wryly. “If you could force [government] to spend all its attention inwardly on quelling mass disruption or civil unrest… then they have much less political capital, and much less physical capital, to put towards an external-facing threat.”
Water, water everywhere, but not enough to drink
In countries like the UK, it has been tricky to put together pre-emptive actions against grey-zone threats, not because there isn’t enough data, but because so much of it is siloed.
There are tens of thousands of cameras set up across the UK, Mead noted, but camera footage from any single CCTV network is typically not regularly observed, let alone run through systems that might compare it with other video data, or activity on social media or other channels, to find patterns of activity.
“London has more CCTV than anywhere else on the planet,” Mead said. “None of it is connected.”
By the time an incident has occurred and it’s being investigated, the perpetrators have often already left the country.
“You are looking at maybe two, three months to pull together specific evidence,” he said. “Our sensing infrastructure is not coordinated. I think there’s a general belief that, okay, we put up more cameras, we put up more sensors, then we could solve this issue, but unfortunately, we don’t have time.”
Augur works with private and public safety organisations to set up better systems for ingesting and “reading” the data that is generated through CCTV and other networks, and then uses AI to match this up with other data to help surface patterns in activity. Mead indicated that talks with decision makers on buying more technology help with the work have become more serious in recent times.
But this touches on another important point: data protection. Recent changes in UK law, specifically the DUAA, have made it smoother for law enforcement and national security to link up how previously-siloed data can be used to in aid of their work. However, the public and privacy groups have been very vocal against some of the changes.
“I think the critical thing here is is to build the technology from the ground up, understanding exactly what the requirements are within, within society,” Mead said. “You have to earn the right to be able to deploy these things. I think we’ve seen certain examples of of people who’ve taken a slightly flippant approach to security here.”